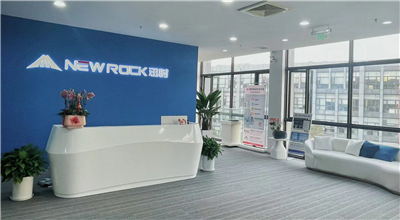
New Rock is a digital solution provider of intelligent VoIP communication and cloud services, with products such as VoIP gateway, IP phone, IP-PBX, call recording solution, audio and video conferencing system, etc.
Together with our agents and distributors, we provide convenient local service and quality after-sales maintenance service. The standard service provided is 5×8 (5 days a week, 8 hours a day) technical service support, providing customers with maintenance, repair and remote technical support services through phone and e-mail.
(New Rock Technologies, Inc.) is a new generation of intelligent communication equipment and solution provider. We provide future-oriented intelligent communication products and services to customers such as telecom operators, governments, enterprises, etc.
Since the establishment 19 years ago, New Rock has always taken R&D as our core mission and insisted on independent innovation. New Rock has more than 80 certificates and honors, with 19 years of industry brand recognition and influence, and is the common choice of many customers!
New Rock has established a nationwide service system with Shanghai headquarters as the center and six branches or offices in Beijing, Guangzhou, Shenzhen, Shandong, Wuhan and Chengdu to provide customers with perfect pre-sales consultation and after-sales service.
VoIP Compliance for European Financial Institutions:MiFID II&GDPR Guide
European financial institutions operate in one of the world’s most regulated communication environments.With MiFID II,GDPR,and country-specific rules,navigating compliance is complex—but critical.Voice over Internet Protocol(VoIP)systems,when configured correctly,can simplify adherence to these regulations while enhancing communication efficiency.
MiFID II:The Backbone of EU Financial Communication Rules
MiFID II(Markets in Financial Instruments Directive II)sets strict standards for communication in financial markets,with VoIP systems playing a central role:
-Call Recording Mandate:All"relevant communications"—including voice calls,video chats,and even instant messages related to trades—must be recorded and retained for 7 years.This applies to banks,brokers,and investment firms operating in the EU.
-Data Integrity:Recordings must be tamper-proof and easily retrievable for regulatory audits.Altered or lost recordings can result in fines(up to€5 million or 10%of annual revenue,whichever is higher).
-Real-Time Monitoring:Firms must monitor communications for market abuse(e.g.,insider trading),requiring VoIP systems to flag suspicious calls(e.g.,sudden spikes in trading-related conversations).
GDPR:Protecting Customer Data in VoIP Systems
The General Data Protection Regulation(GDPR)adds another layer of complexity,focusing on the privacy of personal data(e.g.,customer names,account details)transmitted via VoIP:
-Data Minimization:VoIP systems must collect only necessary data(e.g.,avoid recording non-financial calls unless required).
-Data Sovereignty:Personal data of EU residents must be stored within the EU or in countries with"adequate"data protection laws(e.g.,Japan,Canada).Cloud VoIP providers without EU data centers risk non-compliance.
-Subject Access Rights(SARs):Customers can request copies of their call recordings,requiring systems to quickly retrieve specific files—often within 30 days.
Building a Compliant EU VoIP System
To meet MiFID II,GDPR,and other EU rules(e.g.,Germany’s BaFin guidelines),financial institutions need VoIP systems with these features:
1.Automated,Encrypted Recording:
-Triggers recording for trade-related calls(via keyword detection or department tagging).
-Encrypts recordings in transit(SRTP)and at rest(AES-256)to prevent unauthorized access.
2.Local Data Storage:
-Hosts recordings in EU-based data centers(e.g.,Frankfurt,Dublin)to comply with GDPR’s data sovereignty rules.
-Avoids cross-border data transfers unless explicit customer consent is obtained.
3.Audit-Ready Tools:
-Generates tamper-proof logs of all recording activities(who accessed a file,when,why).
-Supports advanced search(by date,caller ID,keywords)to quickly respond to SARs and regulatory inquiries.
4.Granular Access Controls:
-Limits recording access to authorized staff(e.g.,compliance officers,legal teams)via role-based permissions.
-Tracks every access attempt for GDPR accountability.
Case Study:EU Bank Compliance with New Rock
A major French bank with 50+branches needed to replace its legacy PBX to meet MiFID II and GDPR.It deployed NewLync 2.0 with:
-Local servers in Paris for call storage(GDPR compliance).
-Automated recording of trading desk calls,with 7-year retention(MiFID II).
-Encrypted retrieval tools for SARs,reducing response time from 10 days to 48 hours.
The result?Successful BaFin audits and zero GDPR fines,with improved communication efficiency across branches.
2025 Outlook:Evolving EU Regulations
EU regulators are increasingly focusing on AI and real-time monitoring.Future VoIP systems will need to integrate AI-driven anomaly detection(to flag market abuse)and enhanced encryption(e.g.,post-quantum cryptography)to stay compliant.
For European financial institutions,compliant VoIP isn’t just a box to check—it’s a foundation for trust and operational resilience.